Reputation Management
Fixing Search Filtering and Optimization Issues on ContentKeeper Networks

Aug
Fixing Search Filtering and Optimization Issues on ContentKeeper Networks
ContentKeeper Search Optimization Starts With Clear, Granular Policies
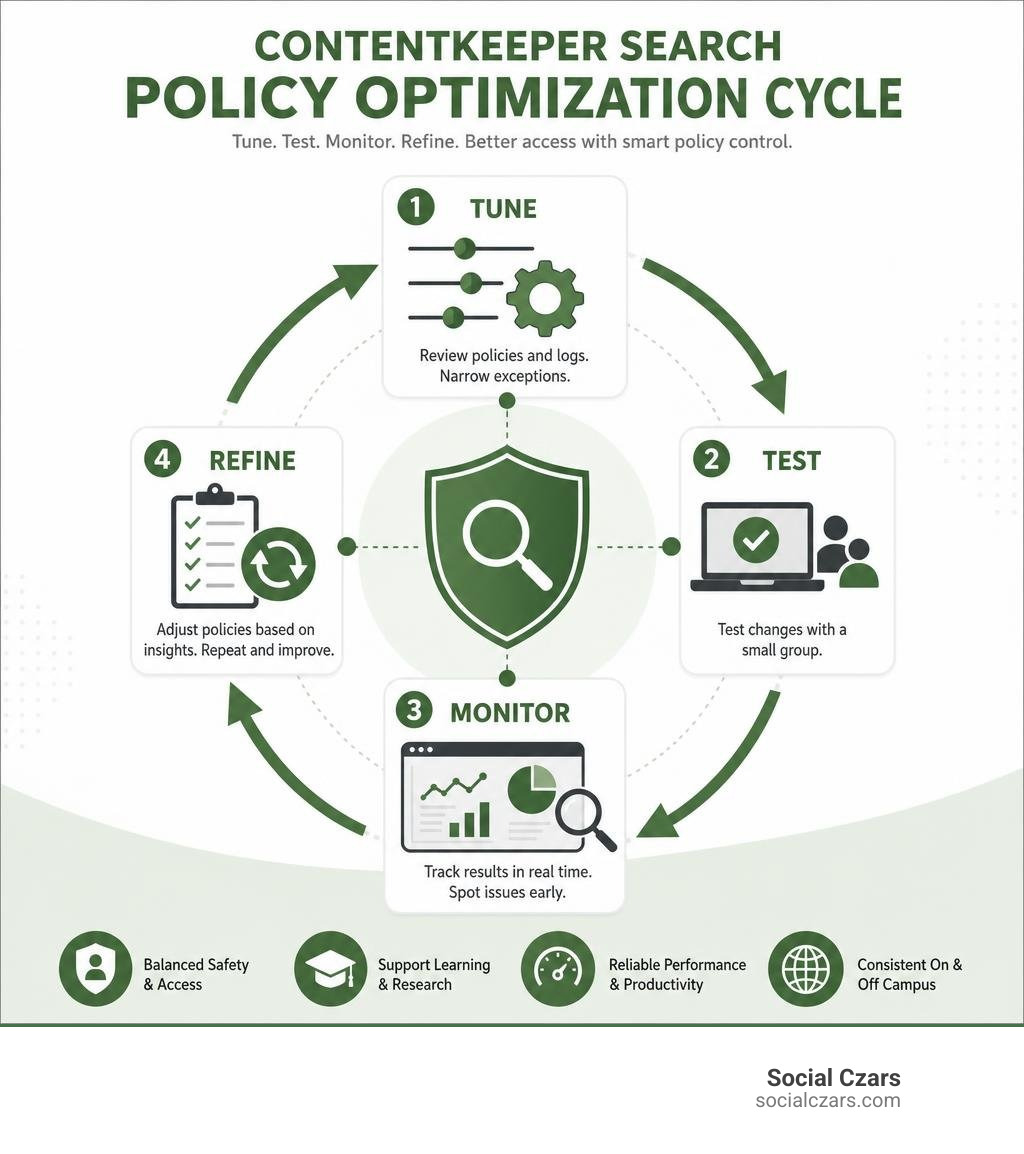
ContentKeeper search optimization means tuning filtering rules so safe-search controls, DNS policies, and SSL inspection protect users without blocking legitimate results or slowing access. Start by reviewing blocked-search logs, identifying the exact policy or category causing false positives, and then using the narrowest possible exception – such as a specific domain, subdomain, or approved educational URL – rather than weakening a district-wide rule.
For consistent results across campus, home, and BYOD devices:
- Confirm SafeSearch and age-appropriate search restrictions are applied to supported search and video platforms.
- Check that SSL inspection certificates are trusted on managed Windows, macOS, iOS, and ChromeOS devices.
- Use cloud-based policies for off-campus traffic to avoid routing remote browsing back through an on-premise network.
- Review real-time dashboards and forensic logs for blocked domains, policy conflicts, unusual bandwidth use, and attempted VPN bypasses.
- Test changes with a small group before applying them broadly.
The goal is not simply to block more. Strong filtering balances CIPA-related safety obligations with reliable access to legitimate learning, research, and communications resources. ContentKeeper supports cloud, hybrid, and on-premise approaches, with cross-platform controls and cloud filtering designed to extend policies beyond the school network.
I am John DeMarchi, founder of Social Czars, with experience in SEO, digital reputation strategy, and the changing relationship between AI, search access, and online visibility. In this guide to ContentKeeper search optimization, I will focus on practical ways to reduce filtering friction while preserving policy control.
Contentkeeper search optimization word list:
Understanding Web Filtering and ContentKeeper Search Optimization
Modern web filtering environments require a balance between security and open access. When networks deploy secure web gateways, the system actively intercepts web traffic to identify malicious domains, enforce organizational standards, and log user activity. Enterprise platforms like ContentKeeper must process immense amounts of data while keeping latency minimal.
When network configurations are misaligned, search engines often become the first point of failure. Overly restrictive filters frequently misinterpret legitimate search queries as policy violations. For organizations managing public-facing profiles, resolving these issues aligns closely with implementing custom SEO strategies that ensure educational, professional, and brand assets remain fully visible and accessible.
How ContentKeeper Enforces SafeSearch and DNS Policy Rules
SafeSearch enforcement operates across multiple network layers. When a user submits an organic query via Google, Bing, or Yahoo, the filtering engine evaluates the request before the remote host renders results.
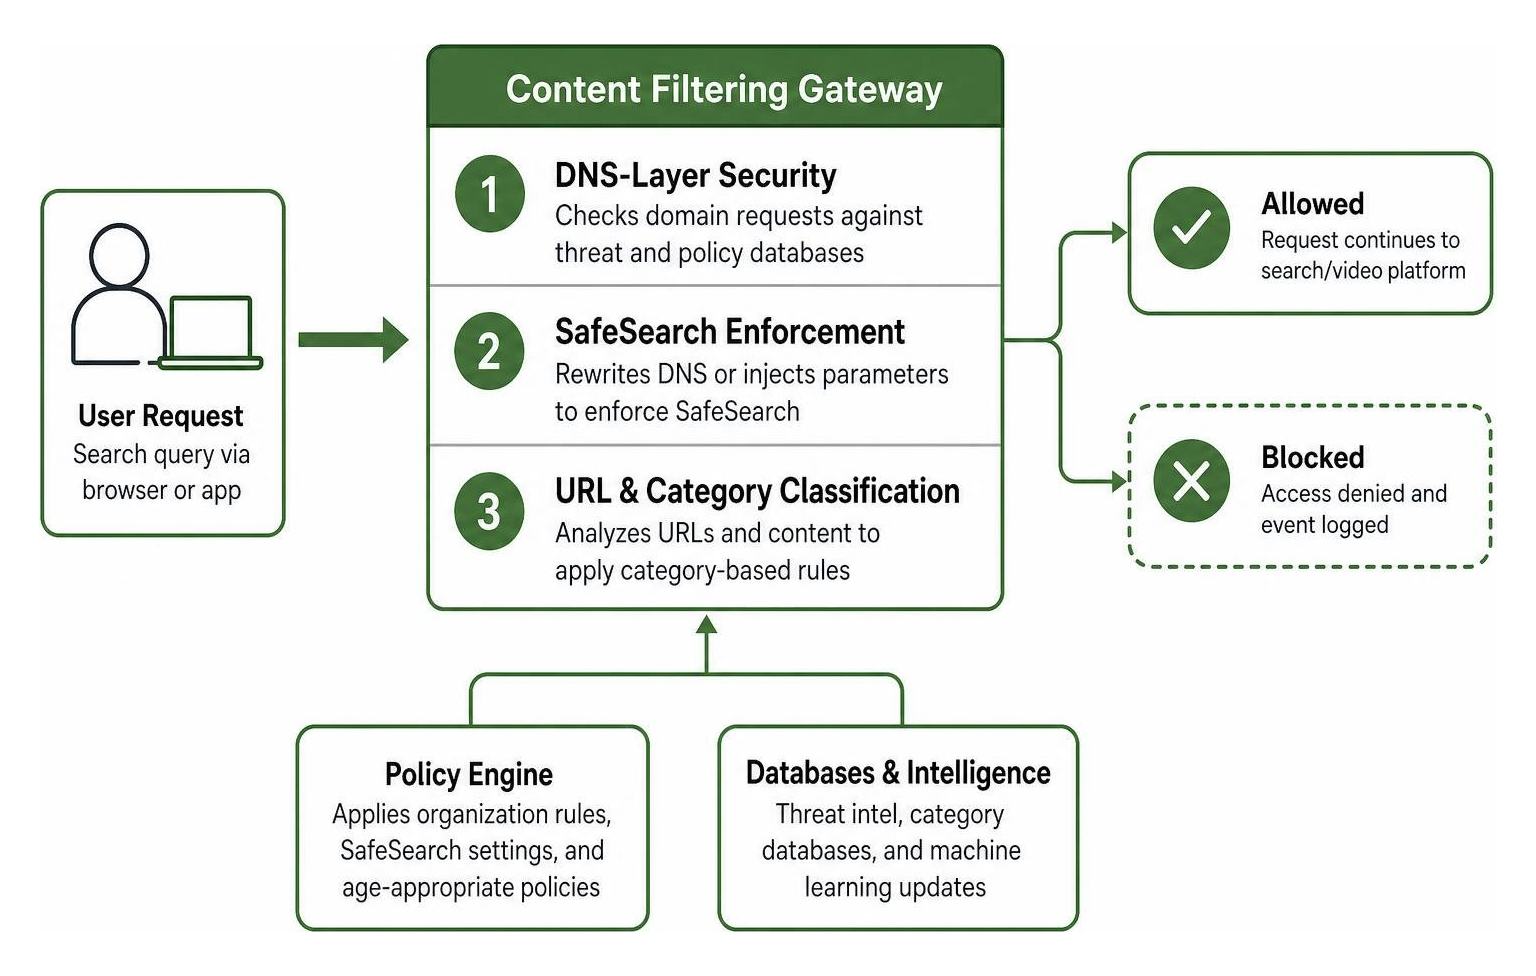
- DNS-Layer Security: The gateway checks domain-level requests against broad threat databases. If a query routes to an untrusted IP address or unauthorized domain, the connection terminates before establishing a full handshake.
- Search Rewriting and Parameter Injection: To enforce strict SafeSearch rules, the appliance transparently rewrites DNS records or injects parameters into the outbound HTTP/HTTPS request (such as directing queries to
forcesafesearch.google.com). - URL and Category Classification: The engine assigns category tags based on automated database listings and real-time machine learning analysis to block inappropriate or adult material.
The Technical Architecture of ContentKeeper Search Optimization
To manage traffic without causing browser timeouts, the filtering appliance relies on a multi-tiered proxy and SSL decryption framework. Because the vast majority of web traffic is encrypted via HTTPS, shallow packet inspection cannot identify the specific keyword parameters within a search string.
Deep packet inspection (DPI) requires managed client devices to trust an organizational Root Certificate Authority (Root CA). This enables the filter to execute transparent TLS proxy operations, decrypting headers to enforce strict search policies and re-encrypting the data before it reaches the endpoint. Understanding these technical layers helps organizations align their internal network security with clear digital design principles, much like optimizing Search Engine Optimisation (SEO) and content architecture for external web crawlers.
Step-by-Step Guide to Resolving Search Filtering and Latency Errors
When search queries lag or fail across enterprise networks, systematic troubleshooting isolates whether the bottleneck stems from certificate mismatches, incorrect DNS routing, or conflicting policy rules.
Configuring Granular SSL Inspection and Certificate Settings
Without a properly installed root certificate, browsers flag decrypted search engine traffic as an invalid SSL connection, triggering browser warning screens and broken search result displays.
- Generate and Export the Root CA: Access the administrative console, generate an organization-specific Root CA, and export the
.crtor.pemfile. - Distribute via MDM/GPO: Deploy the certificate to the Trusted Root Certification Authorities store across all managed endpoints using Group Policy Objects (GPO) for Windows, Google Admin Console for ChromeOS, or Apple Configurator/JAMF for macOS and iOS.
- Set Up Domain Exceptions: Exclude sensitive domains that utilize strict certificate pinning (such as specific banking portals, Apple ID authentication servers, and software update endpoints) from full SSL decryption to prevent service disruption.
Implementing ContentKeeper Search Optimization for Multi-Platform Devices
Modern institutions support heterogeneous operating system environments. Rather than relying entirely on browser extensions that can be disabled by users, platform administrators should deploy lightweight client agents tailored for each OS:
- Windows and macOS: Install the designated agent service to handle local DNS routing and enforce policy execution across all installed desktop browsers.
- ChromeOS: Deploy managed user policies directly via Google Workspace Admin, locking down developer tools, unauthorized extensions, and private DNS overrides.
- iOS and iPadOS: Implement unified MDM profiles featuring supervised device configurations to enforce global HTTP proxy routing on managed school devices.
Preventing Over-Blocking and Calibrating Search Keyword Whitelists
Over-blocking occurs when broad category filters intercept harmless terms within search strings, preventing users from accessing legitimate educational or scientific material.
| Filtering Level | Scope of Control | Typical Risk | Recommended Best Practice |
|---|---|---|---|
| Broad Category Blocking | Restricts entire domain groups (e.g., Gaming, Social Media). | High rate of false positives on blended educational platforms. | Use dynamic time-based policies rather than 24/7 blanket bans. |
| Subdomain Rules | Allows specific sub-properties while restricting the parent domain. | Moderate risk of accidental exposure if sub-paths are complex. | Whitelist specific educational domains like scholar.google.com. |
| Keyword Interception | Flags raw text strings within search queries and URLs. | Over-blocks medical, literary, and historical academic research. | Pair keyword monitoring with context-aware semantic evaluation. |
| Granular Whitelisting | Grants explicit, high-priority pass-through for verified resources. | Low; requires periodic administrative review. | Create targeted rule exceptions for certified educational content. |
Managing Search Visibility and Access Across Hybrid Networks
With remote learning and off-campus connectivity standard in August 2026, network visibility must extend beyond physical on-premise firewalls. Cloud-native filtering architectures allow client agents to query security nodes directly, eliminating the need to backhaul traffic to local data centers and reducing latency.
Districts can optimize their internal network settings while using advanced SEO strategies to maintain digital clarity and ensure authorized assets remain accessible across external web platforms.
Balancing CIPA Compliance with Open Educational Search Access
The Children’s Internet Protection Act (CIPA) requires certified institutions in the United States to filter visual depictions of obscenity, child pornography, and material harmful to minors to maintain eligibility for E-rate funding discounts.
To satisfy compliance guidelines without disrupting research:
- Implement role-based access control (RBAC), applying strict restrictions to primary grade tiers while granting broader research permissions to advanced high school or administrative accounts.
- Enforce strict SafeSearch parameters across major search interfaces alongside contextual YouTube filtering to allow instructional videos while stripping distracting comment feeds.
- Align access protocols with verified online presence optimization practices to maintain transparent public and institutional communication.
Monitoring Real-Time Forensic Logs and Search Analytics
Real-time logging provides administrators with actionable data to refine filtering rules, detect security threats, and protect digital wellness.
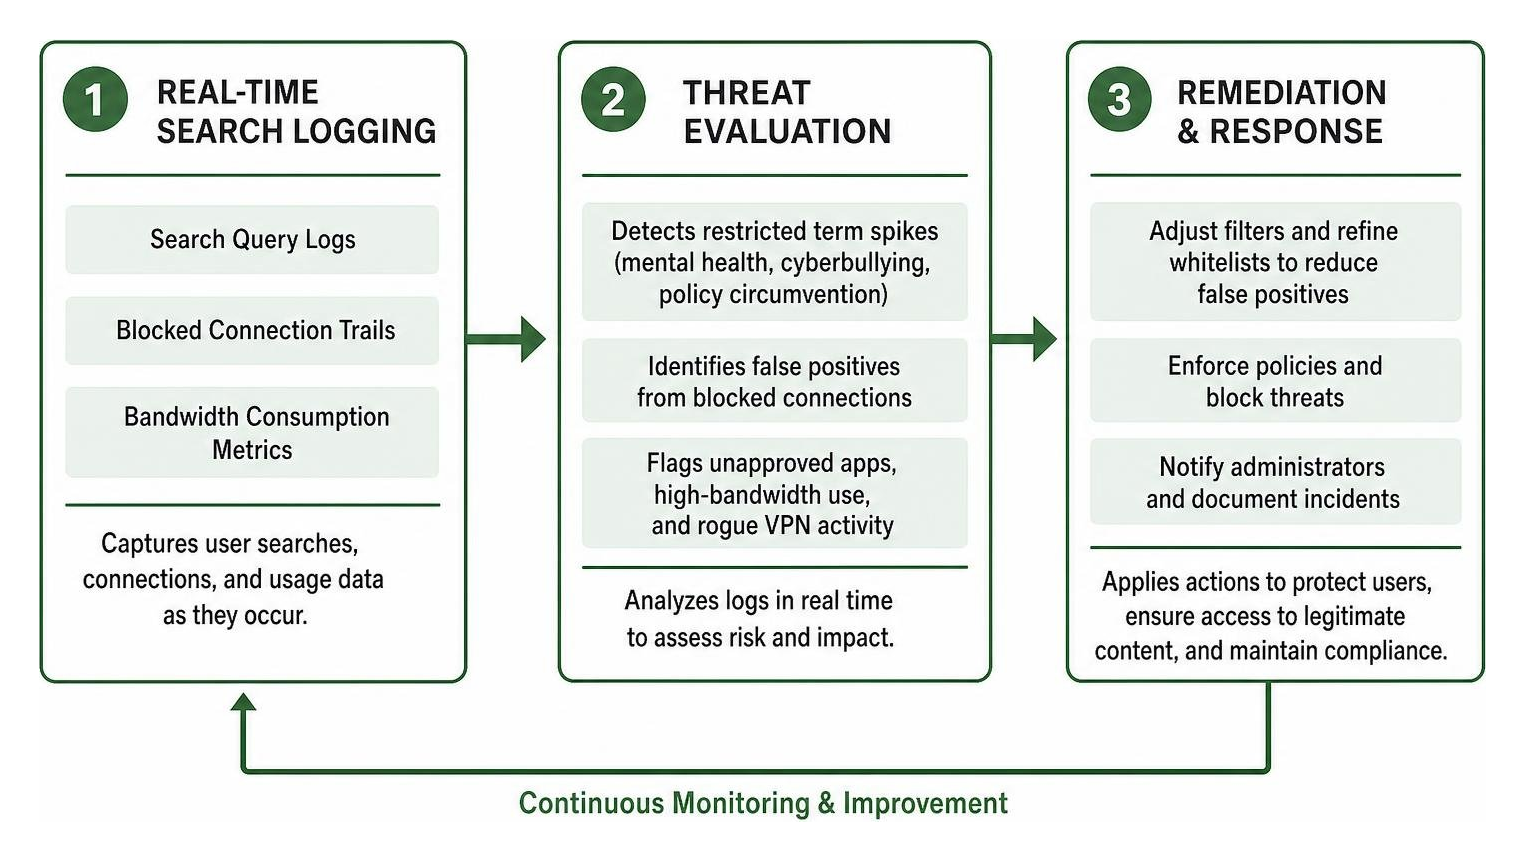
Key diagnostic metrics to track within your analytics dashboard include:
- Search Query Logs: Identifies sudden spikes in restricted search terms, flagging potential mental health crises, cyberbullying, or policy circumvention attempts.
- Blocked Connection Trails: Highlights frequent false positives to help administrators fine-tune whitelists.
- Bandwidth Consumption Metrics: Identifies unapproved peer-to-peer applications, high-bandwidth streaming, or rogue VPN services attempting to tunnel through standard web ports.
- Device Authentication Logs: Validates that all off-campus hardware properly checks into the cloud proxy, an essential element of ongoing digital footprint management.
Frequently Asked Questions About ContentKeeper Search Settings
Why are legitimate search results being blocked on student devices?
Legitimate queries are typically blocked due to overly broad category rules, aggressive keyword blacklists, or SSL handshake failures. When a search string contains a substring that matches a banned term, category-based filters may block the entire page. Ensuring root certificates are correctly deployed and adding explicit subdomain exceptions resolves the majority of these false positives.
How do administrators enforce SafeSearch across Google, Bing, and YouTube?
SafeSearch enforcement is typically managed through DNS CNAME redirection or automated header injection. By mapping standard search domains (such as www.google.com) to their designated SafeSearch hostnames (such as forcesafesearch.google.com) at the DNS gateway layer, the appliance ensures that all client queries return filtered results, regardless of browser privacy modes.
How can schools resolve search latency on off-campus BYOD devices?
Off-campus latency generally occurs when mobile devices are configured to backhaul all web traffic through an on-premise gateway via traditional VPN tunnels. Transitioning to a distributed cloud filtering model allows endpoints to query regional cloud nodes directly, significantly lowering ping times and eliminating local network bottlenecks.
Conclusion
Maintaining a secure, high-performing network requires ongoing governance, balanced filtering policies, and routine log auditing. By optimizing DNS policies, deploying root certificates across all endpoints, and replacing blunt category blocks with granular keyword exceptions, IT teams can maintain full safety compliance while providing unimpeded access to critical online resources.
If your organization is reviewing its current network controls, exploring alternative web filtering frameworks, or learning how to get rid of ContentKeeper restrictions to improve network performance, establishing a structured policy audit is the most effective path forward.
